Fake Payment UPI App for Android: Download Latest APK
Fake Payment UPI App for Android: Download Latest APK queries target unverified file repositories, Telegram channels, and modding blogs offering counterfeit financial applications. These modified packages claim to provide offline receipt simulation, editable wallet balances, and custom transaction displays without connecting to legitimate banking infrastructure. Because Android permits manual side-loading of APK files outside the official Google Play Store, understanding the technical architecture, security vulnerabilities, malware hazards, and legal consequences associated with these downloads is essential for mobile device safety.
The software marketed across unverified web portals as a Fake Payment UPI utility consists of unauthorized Android packages engineered to replicate the user interface, typography, color schemes, and transaction summary views of major digital wallets. Unlike genuine payment software connected to the Unified Payments Interface (UPI) network governed by the National Payments Corporation of India (NPCI), this modified software runs entirely on local, client-side scripts. It allows users to manually input arbitrary monetary values, fake recipient names, and custom reference IDs to generate static image receipts or screen animations designed to deceive store owners and merchants.
What Advertised “Features” Are Claimed by Modded APKs?
Promotional material for counterfeit payment APKs on unverified forums and Telegram channels frequently lists several core capabilities to attract users:
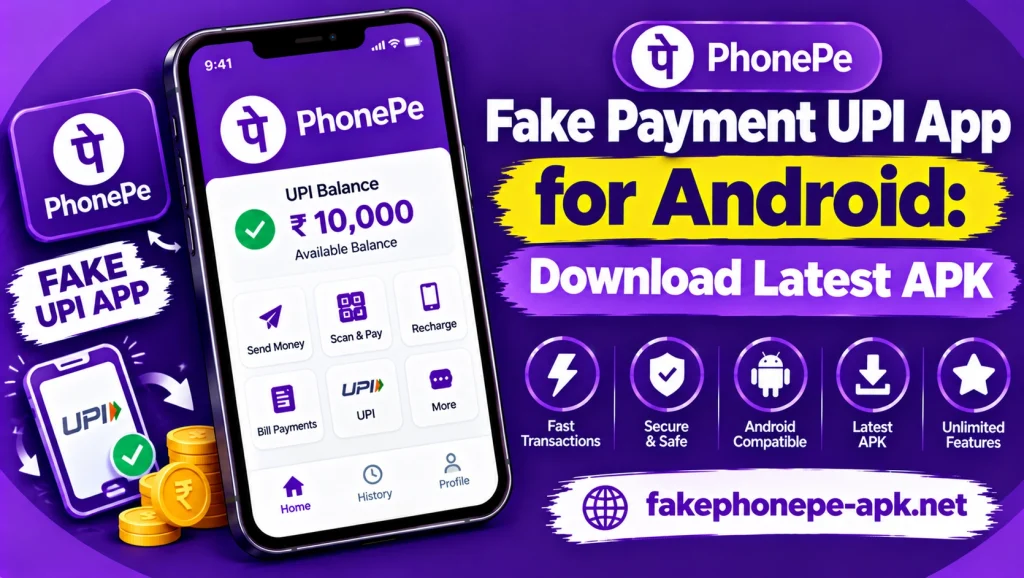
- Customizable Transaction Amounts: The software allows users to manually type any arbitrary monetary figure into an input box to display on screen.
- Editable Recipient Names and VPAs: Operators can input custom merchant names and fake Virtual Payment Addresses (VPAs) to mimic specific retail business profiles.
- Simulated Success Animations: The app renders mock checkmarks, success banners, and interface layouts modeled after genuine payment confirmation screens.
- Offline Mocking Scripts: The interface operates without active network requests, allowing users to generate receipt screens without internet connectivity.
Major Risks of Downloading and Installing Modded APKs
Fake Payment UPI App for Android: Download Latest APK packages hosted on third-party forums, Telegram channels, and unverified blogs bypass official security vetting and introduce severe device vulnerabilities:
- Injected Trojan Malware and Spyware: Modded financial packages are routinely bundled with Remote Access Trojans (RATs), keyloggers, and background adware that monitor user activity, record keystrokes, and capture sensitive credentials.
- SMS Interception and OTP Bypassing: Unauthorized applications frequently request broad SMS permissions, allowing remote operators to silently intercept banking One-Time Passwords (OTPs) and compromise legitimate financial accounts.
- Data Harvesting and Credential Theft: Entering contact numbers, personal names, or mock account credentials into unverified APKs exposes device data to external command-and-control servers operated by cybercriminals.
- Severe Legal Liabilities: Possessing, testing, or deploying software explicitly engineered to generate fraudulent transaction proofs and deceive businesses constitutes cyber fraud under financial crime laws, exposing individuals to police investigation and bank account freezes.
Technical Comparison: Official App vs. Fake APKs
To understand why downloading modded financial packages introduces critical system vulnerabilities, review the following security parameters:
| Security Parameter | Official UPI Payment Application | Counterfeit Payment APK Mod |
| Distribution Channel | Google Play Store / Apple App Store | Unverified third-party file hosts and channels |
| Security Vetting | Audited, sandboxed, and scanned by Play Protect | Zero security checks; high probability of malware |
| Data Protection | Enterprise-grade end-to-end encryption | Unencrypted data logging and credential scraping |
| System Permissions | Strictly limited to essential device functions | Demands dangerous accessibility and overlay rights |
What to Do If You Have Already Downloaded the File
If an unauthorized or counterfeit package has already been installed on your Android hardware, executing immediate cleanup steps is essential to safeguard your personal data:
- Disconnect Network Connectivity: Turn off Wi-Fi and mobile data immediately to prevent active background scripts from transmitting collected data to remote servers.
- Uninstall the Application: Open Settings > Apps, locate the suspicious utility, force stop its process, and select Uninstall.
- Delete Residual Files: Open your Android File Manager, access the Downloads directory, and permanently erase the installer
.apkfile. - Revoke Accessibility and Overlay Rights: Navigate to Settings > Accessibility and ensure no unverified third-party tools retain active system-level permissions.
- Run a Full Security Scan: Perform a comprehensive system scan using Google Play Protect or a trusted mobile antivirus suite to clear remaining background threats.
Conclusion
Fake Payment UPI App for Android: Download Latest APK offers are dangerous malicious traps engineered to exploit side-loading permissions, infect Android smartphones with spyware, and harvest sensitive financial credentials. Because these counterfeit utilities bypass official banking channels and security frameworks entirely, avoiding unauthorized software downloads is the only way to ensure privacy, device integrity, and legal safety.